AI is transforming financial services and the threats aimed at them. Here is how fintech leaders can turn security, compliance and operational resilience into a foundation for responsible growth.
Financial services have always run on trust. In 2026, earning that trust requires more than protecting transactions at the perimeter. Fintech platforms must verify identities in a world of convincing synthetic media, detect increasingly adaptive fraud, govern the use of artificial intelligence, maintain resilient operations across third parties and translate a changing regulatory landscape into controls that work in real time.
The organizations that address these demands as one connected discipline will be better positioned to grow. Security and compliance can no longer be treated as final checkpoints before launch. They must be designed into the platform, the customer experience and the operating model from the beginning.
AI has changed both sides of the risk equation
AI is helping financial institutions analyze behavior, prioritize alerts and automate repetitive compliance work. The same capabilities are also lowering the cost of impersonation and fraud. Synthetic documents, cloned voices, deepfake video and highly personalized social engineering can make traditional identity checks less reliable.
This is no longer a hypothetical risk. Financial regulators have explicitly warned institutions about deepfake-enabled schemes designed to defeat identity verification and authentication. The practical response is not to reject AI. It is to combine multiple signals so that no single document, face, device or transaction determines trust on its own.
Effective defenses increasingly connect identity verification, device intelligence, behavioral analytics, transaction context and human review. Models can identify anomalies at speed, but high-impact decisions still need clear escalation paths, explainability and accountability.
The competitive advantage will not come from using the most AI. It will come from using AI responsibly, with controls that customers, partners and regulators can trust.
AI governance is becoming an operating requirement
As firms use AI in fraud detection, customer support, underwriting, compliance and product operations, they also inherit new questions. What data trained the model? Which decisions does it influence? How is performance monitored? Can the result be explained? What happens when the model drifts, fails or produces an unfair outcome?
Frameworks such as the NIST AI Risk Management Framework and the financial-services profile developed through the U.S. Treasury-led public-private effort give institutions a practical structure: govern, map, measure and manage. The value of these frameworks is not a certificate. It is the discipline of maintaining an inventory of AI use cases, assigning accountable owners, testing controls and keeping evidence that can withstand scrutiny.
For fintech leaders, AI governance should include data lineage, access controls, model validation, change management, human oversight, documented limitations and continuous monitoring. It should also distinguish between low-risk productivity tools and systems that can affect money movement, identity, credit or customer rights.
Compliance must operate at transaction speed
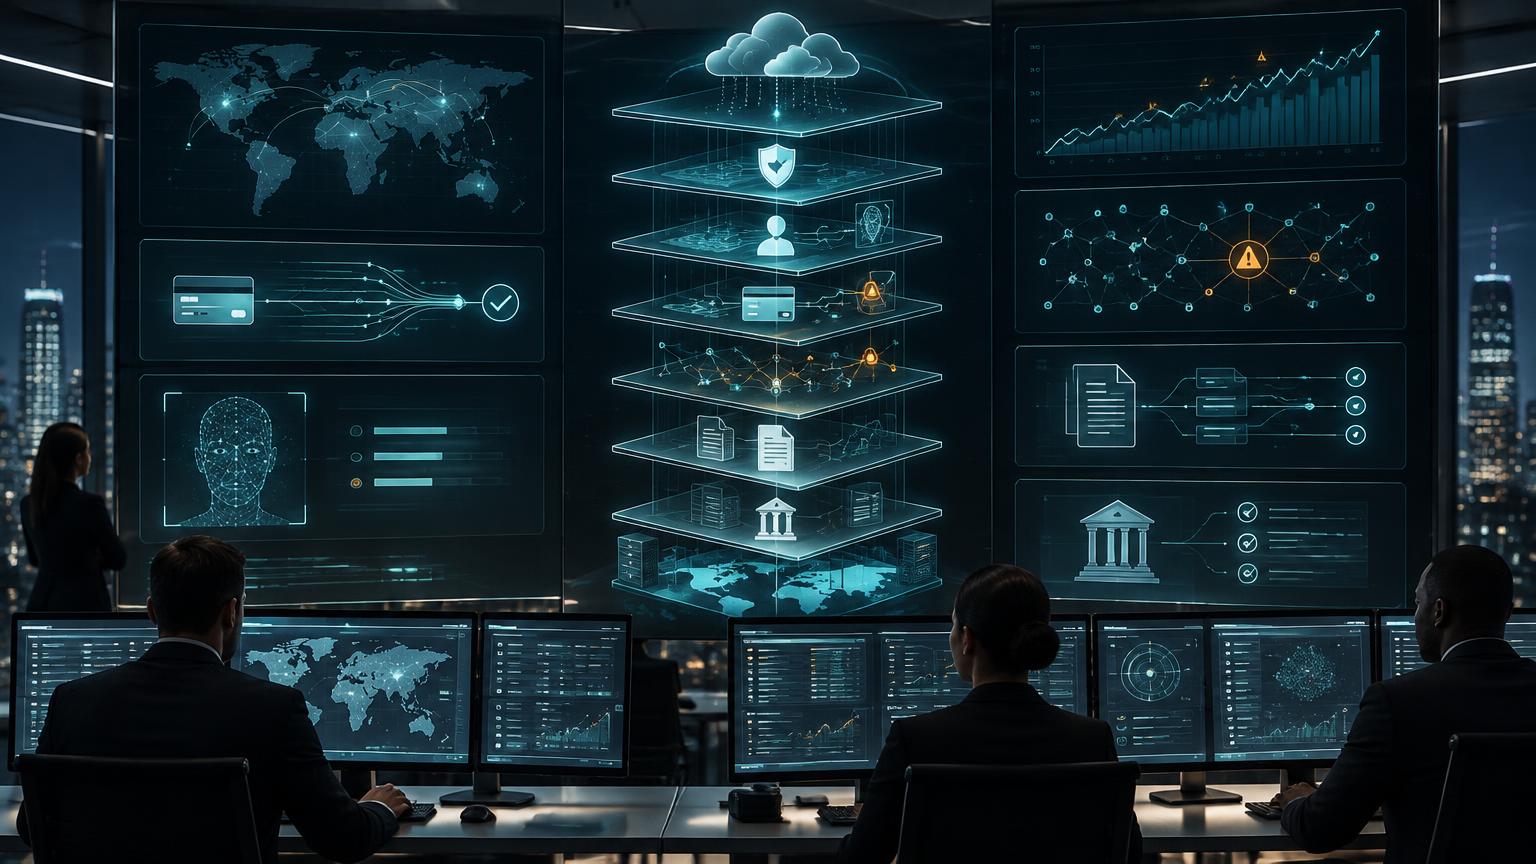
Batch reviews and isolated rule sets are increasingly mismatched with instant payments, digital wallets and always-on global commerce. Fraud and compliance teams need a current view of customer risk, transaction behavior and network relationships while activity is happening.
That does not mean every unusual event should be blocked. Mature monitoring combines rules, analytics and case management to distinguish expected behavior from meaningful risk. It captures the evidence behind decisions, supports escalation and helps teams refine controls without creating unnecessary friction for legitimate customers.
Privacy is part of this design. Collecting more data does not automatically produce better security. Institutions need a clear purpose for each data element, appropriate retention, strong access controls and safeguards that follow sensitive information across systems and providers. The goal is useful intelligence with disciplined data handling.
Operational resilience and third-party risk are converging
Modern fintech is an ecosystem. Cloud services, banking relationships, payment processors, identity providers, data suppliers and software vendors may all participate in a single customer journey. That creates speed and specialization, but it also means a weakness or outage outside the organization can quickly become a customer, compliance and reputational event.
Regulators have made the accountability principle clear: outsourcing an activity does not outsource responsibility. Effective third-party governance covers the full lifecycle, from due diligence and contracting to ongoing monitoring, incident response and orderly exit planning.
The European Union's Digital Operational Resilience Act, now in application, reinforces this direction by bringing technology risk, incident reporting, resilience testing and critical provider oversight into one framework. Even for companies outside the EU, the underlying discipline is useful: understand dependencies, test failure scenarios and design services to continue safely when a provider is disrupted.
Five priorities for fintech leaders
1. Treat identity as a continuous signal. Combine identity, device, behavior and transaction context instead of relying on a one-time check.
2. Govern AI before scaling it. Maintain an inventory, assign owners, test outcomes and document the controls around every material use case.
3. Connect fraud, security and compliance data. Shared context improves detection and reduces duplicated investigations.
4. Engineer for disruption. Map critical dependencies, rehearse incident response and maintain practical recovery and provider-exit plans.
5. Make evidence automatic. Build audit trails, approvals, monitoring results and control records into normal operations rather than assembling them after the fact.
How Fintiv helps clients move from obligation to advantage
Fintiv helps organizations build and operate secure digital financial ecosystems across wallets, payments, loyalty, tokenized assets and connected commerce. Our approach brings product architecture, transaction processing and program operations together so security and compliance are embedded across the customer lifecycle.
For clients, that means designing clear control points from onboarding through funding, payments, rewards, transfers and settlement. It means integrating identity and risk services, applying configurable transaction rules, maintaining traceable records and supporting the operational workflows needed to investigate and resolve exceptions.
Fintiv's platform approach also helps reduce fragmentation. When core wallet, payment and ledger capabilities share consistent data and orchestration, clients gain a stronger foundation for real-time monitoring, reporting and controlled change. Modular integrations allow specialized providers to be incorporated while preserving governance over how data and transactions move through the ecosystem.
This matters when AI is introduced. Reliable AI depends on reliable data, defined permissions and observable processes. By establishing those foundations, Fintiv helps clients use intelligent automation where it adds value while retaining the human oversight and accountability that financial services demand.
Trust is the platform for growth
Security, compliance and customer experience are often described as competing priorities. The strongest fintech programs treat them as mutually reinforcing. Better identity controls can reduce fraud and customer friction. Better data architecture can improve both monitoring and personalization. Better resilience can protect revenue as well as regulatory standing.
The next generation of financial services will be faster, more connected and more intelligent. It will also be judged by how responsibly it manages risk. With security, compliance and resilience built into the platform, fintech companies can innovate with confidence and give customers, partners and regulators a reason to trust what comes next.